 Black Triangle
Teenager Gained Access to 17 Trillion Microsoft Data Rows
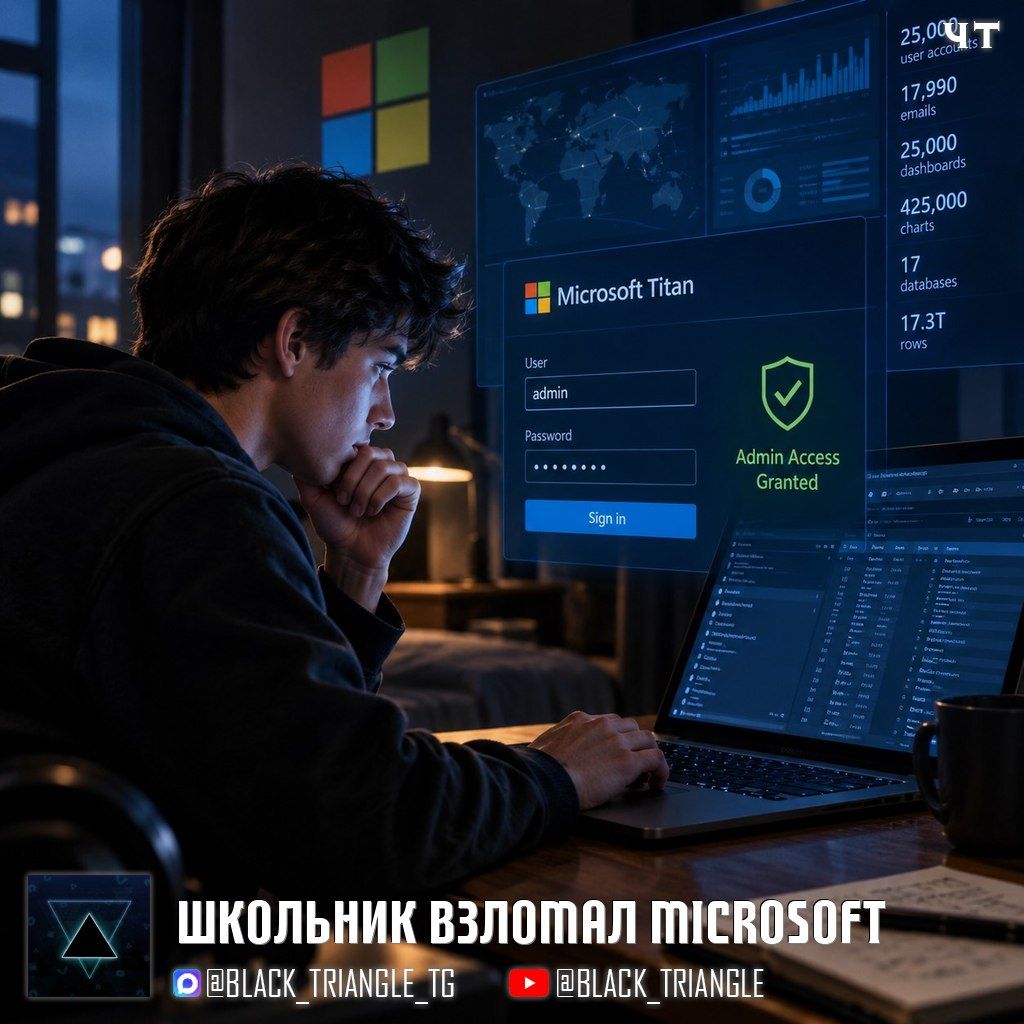
Sixteen-year-old security researcher Faaw gained access to Microsoft Titan, an internal analytics service containing approximately 17 trillion rows of data.
The vulnerability stemmed from the API's failure to verify JWT token digital signatures. The attacker could create an unsigned token and set the value to "admin" instead of an email address.
The system interpreted this value as a local account with ID 1, which granted administrator privileges.
Despite the presence of the Antares AI hacking bot, automated vulnerability detection failed because the neural network could not anticipate the human logic behind substituting the user field.
As a result of the compromise, data belonging to approximately 25,000 employees was exposed, including their accounts and email addresses.
- Approximately 25,000 dashboards and 425,000 charts
- 17 analytical databases comprising 17.3 trillion rows
Microsoft promptly fixed the error and awarded the researcher a bounty of $5,000 USD.
In exchange for compensation, the company requested that the author soften the description of the breach's scale in his public report.