 Crypto Headlines
Detailed Breakdown of the Bitget Attack: Chronology and Methods
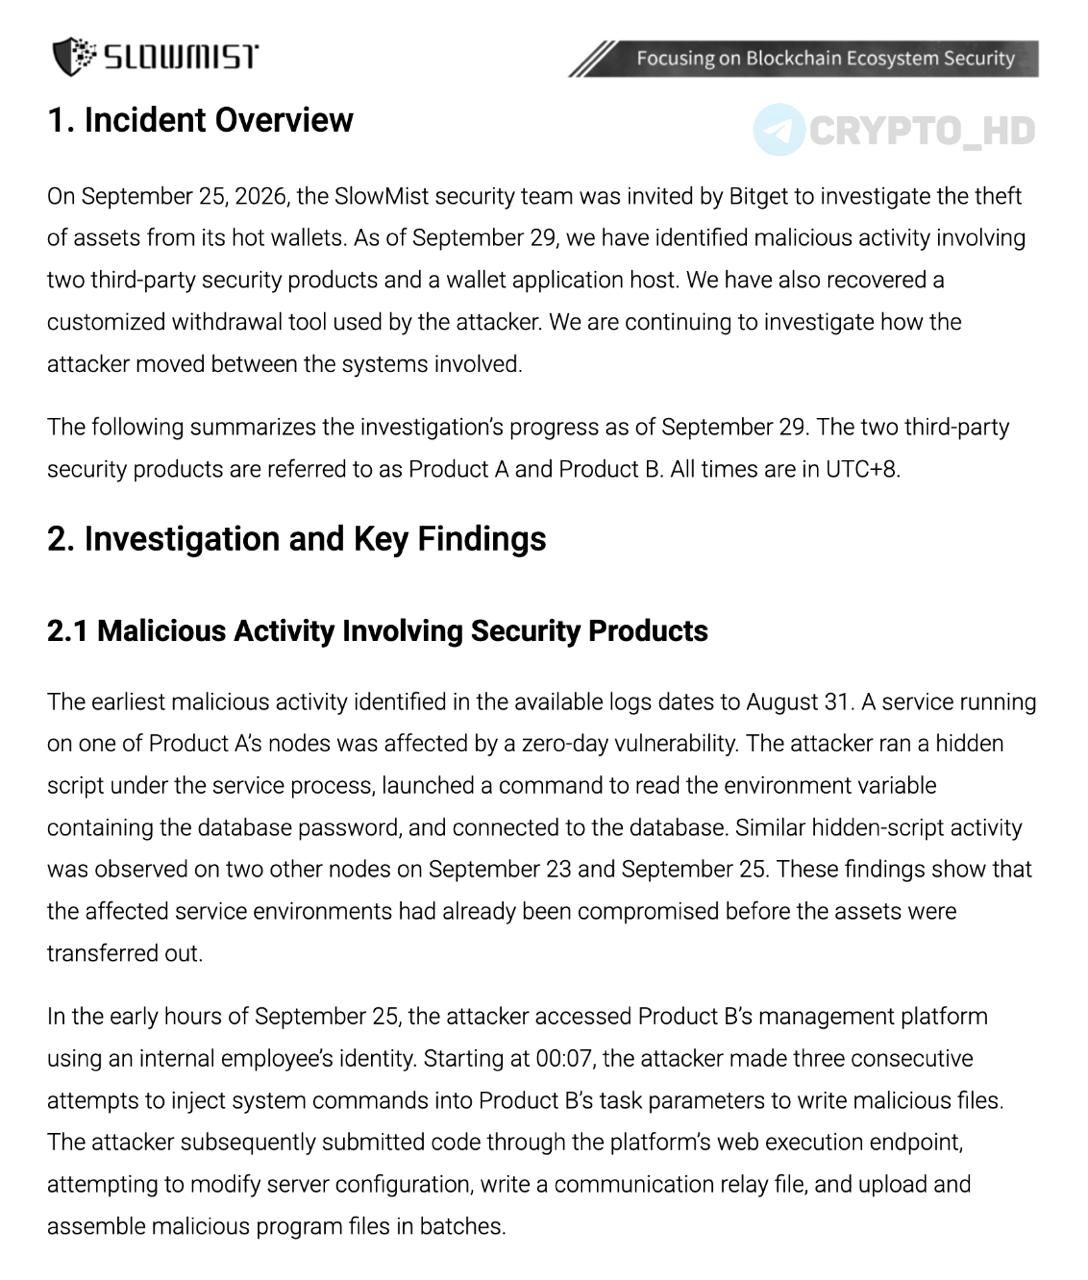
The attack on the Bitget exchange began a month before the theft of funds. The attackers exploited a zero-day vulnerability in a third-party security service.
Attack Timeline
Signs of hacker activity appeared on August 31. The attacker gained access to the service's database via a zero-day vulnerability. Later, malicious activity was detected on two additional nodes.
On September 25, the hacker breached a second security service. They used an employee account to upload malicious files to the system.
Asset Theft Methods
A specialized tool was created for the Bitget system to facilitate the theft. It spoofed risk control parameters and autonomously generated withdrawal requests.
- Asset withdrawals continued for nearly 3 hours
- The process occurred simultaneously across multiple blockchains
- SlowMist is investigating inter-system movements
16.9K views