 Backdoor
ZloyRAT Trojans in GosVPN and RadarBPLA Apps
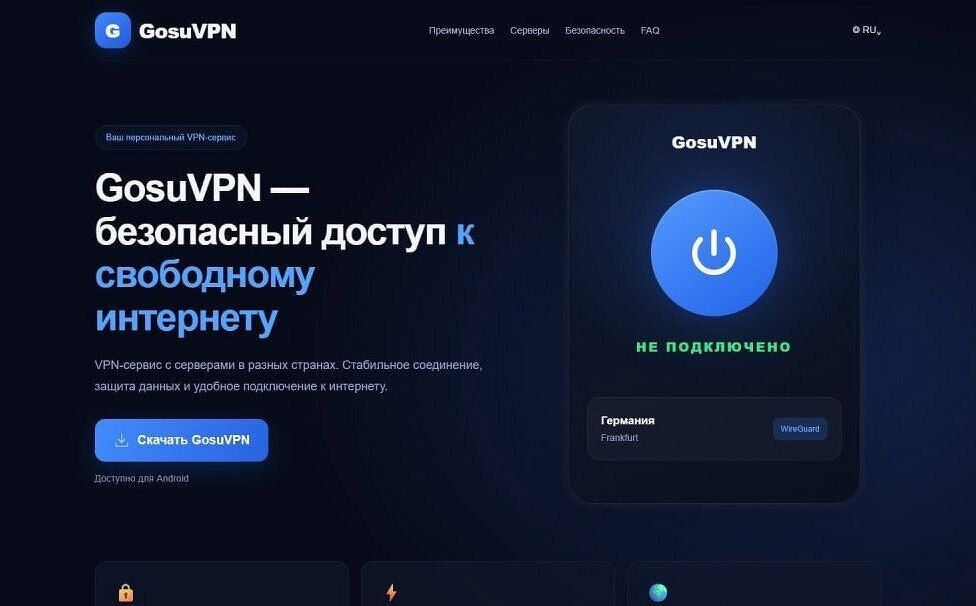
CNews analysts have identified ZloyRAT malware in the GosVPN and RadarBPLA Android apps. Threat actors distribute these APK files via messengers and forums, disguising them as legitimate services.
Once installed, the trojan gains full access to the user's personal data, including SMS messages, contacts, call logs, and Telegram chats. Furthermore, the virus can interact with banking apps and government services, posing critical risks to citizens' financial security.
Fraudsters actively exploit social engineering by leveraging Russians' high reliance on government services and air space monitoring tools. The covert distribution of malicious links makes it difficult for average users to detect the threat in a timely manner.
To protect against such attacks, experts recommend adhering to basic digital hygiene practices: do not download apps from unverified sources and avoid installing third-party APK files. Using only official app stores significantly reduces the risk of trojan infection.
26.2K views