 Crypto Headlines
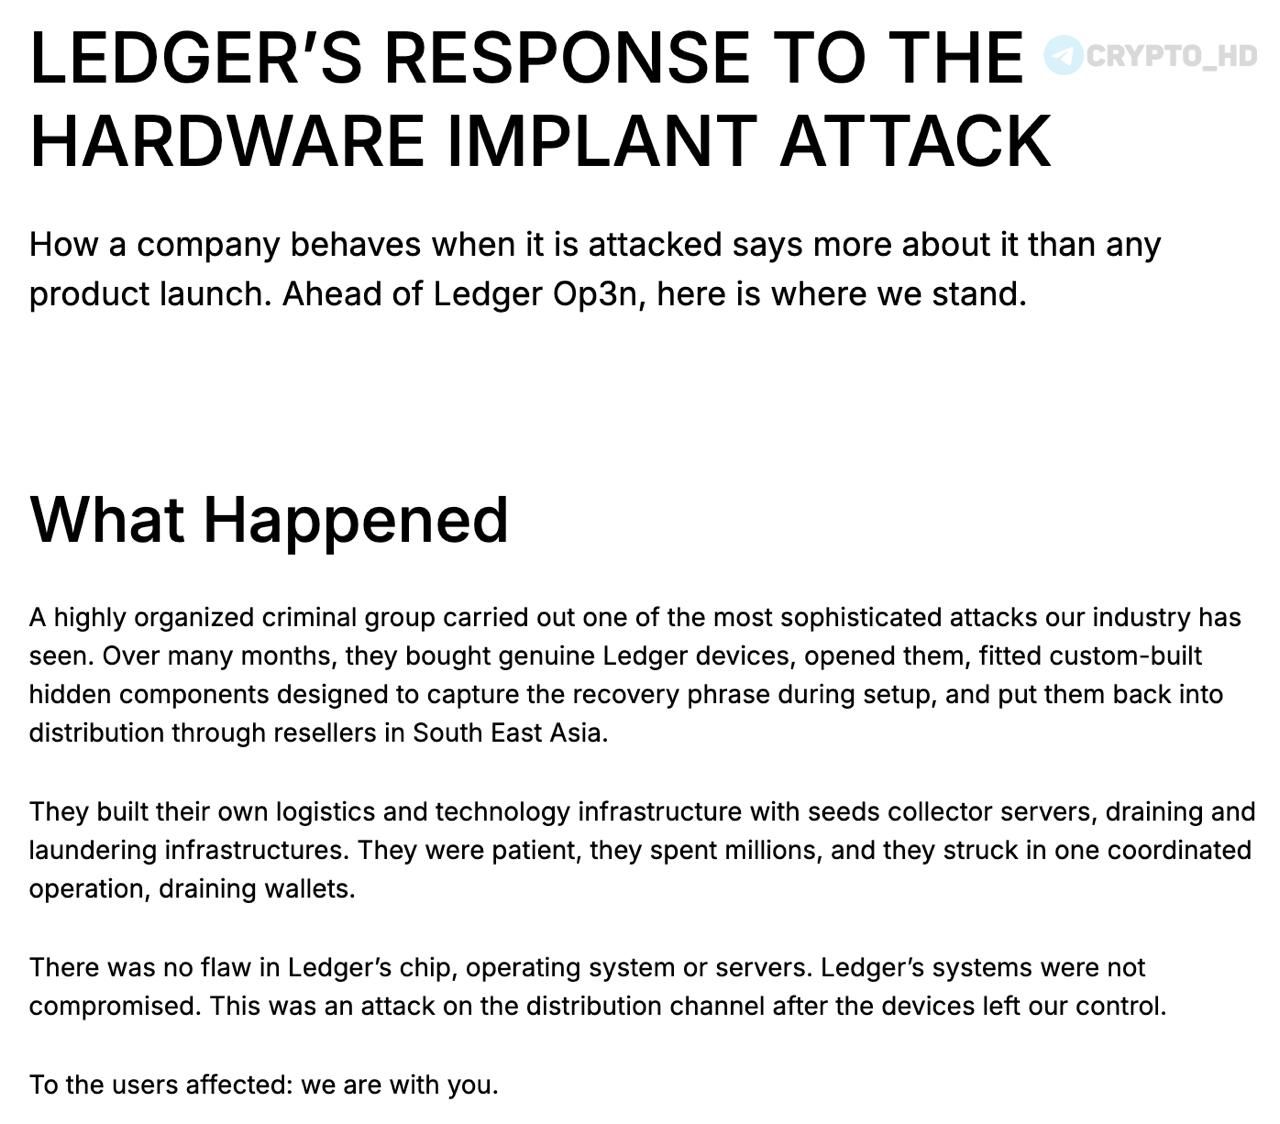
Ledger responds to attack involving implants in wallets
Ledger has responded to a large-scale cyberattack in which a criminal group embedded malicious components into hardware wallets. For months, attackers purchased genuine devices, opened them up, and installed hidden implants to intercept seed phrases.
The modified wallets were returned to sale through resellers in Southeast Asia. The criminals spent millions of dollars preparing the infrastructure for data collection and coordinated theft of users' funds.
No vulnerabilities were found in the devices themselves or in the company's systems.
Following the incident, sales were suspended in Southeast Asia and Hong Kong. Resellers are prohibited from displaying devices on shelves.
- Wallets must be stored separately from display shelves.
- Transfer of devices to buyers is permitted only directly at the time of purchase.
19.5K views