 Crypto Headlines
Hackers substitute crypto addresses via website support systems
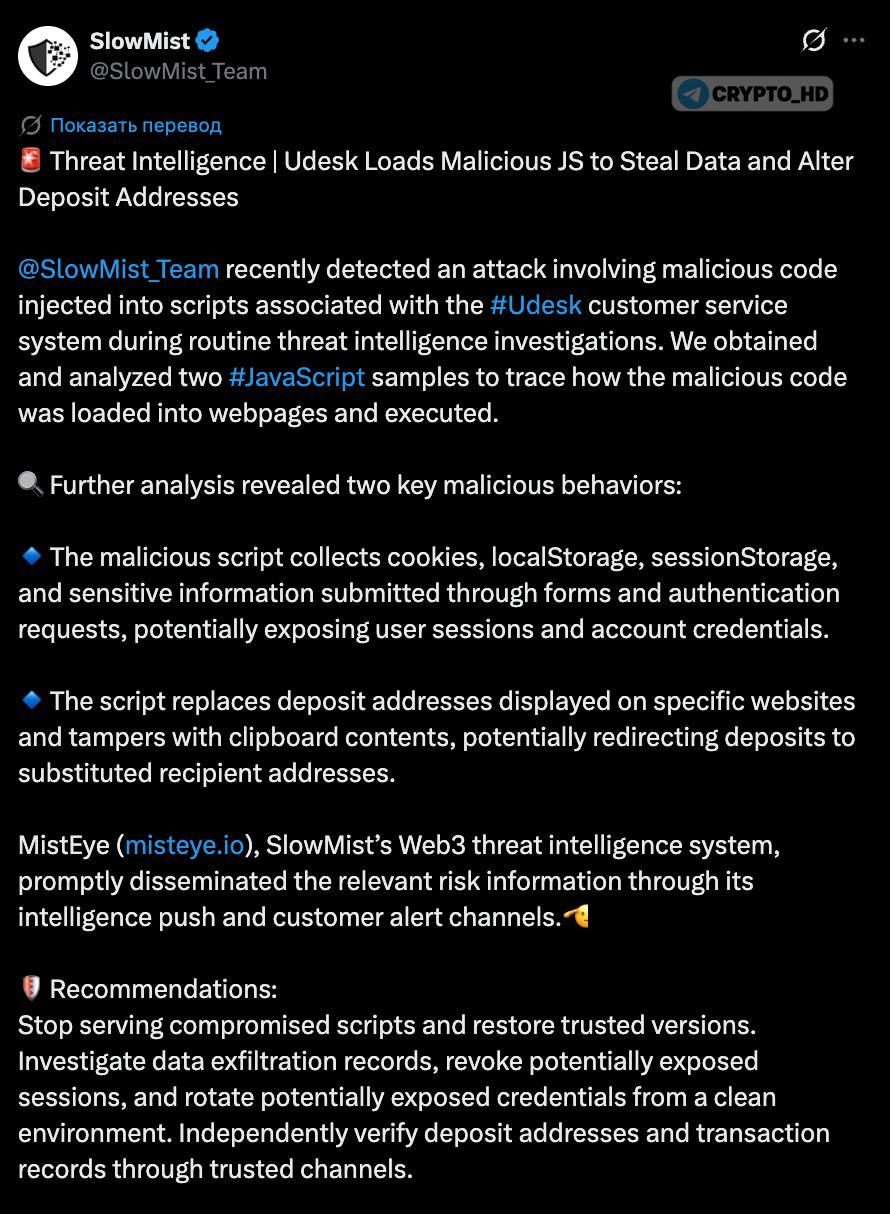
SlowMist specialists discovered malicious JavaScript code in the Udesk customer support system used by many companies, including crypto exchanges. Attackers do not hack websites directly but inject scripts through integrated technical support services.
Address substitution mechanism
The malicious code replaces crypto addresses on deposit pages and in the clipboard. Users may send funds to attackers without noticing the substitution, as they see a fake address instead of the real one.
Personal data theft
Beyond the financial threat, the script collects cookies, login credentials, and form data. This potentially allows attackers to gain access to user accounts across various platforms.
Risks of third-party services
The main danger is that hacking the company's main site is not required for an attack. The malicious code is loaded via an integrated customer support system, such as the Chinese platform Udesk, used for online chats.
Security recommendations
Information about this vulnerability was published by the SlowMist team on social network X. Cryptocurrency users are advised to exercise heightened caution when interacting with sites using third-party support systems.
The vulnerability in the Udesk system highlights the importance of auditing all third-party integrations on financial platforms.
1 views