 Black Triangle
Hacking the Yandex Station via a Certificate Vulnerability
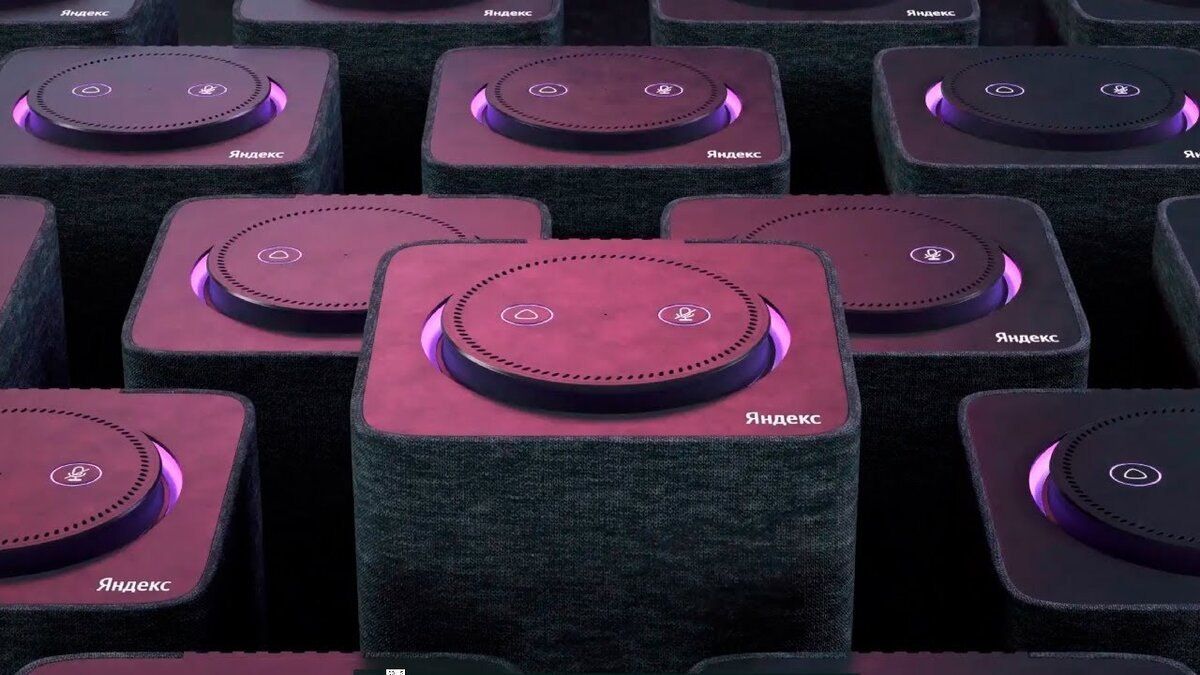
Enthusiasts have released a tool to gain root access to the Yandex Station smart speaker without physical intervention.
The vulnerability is linked to an error in trusted certificates: the device accepted a publicly compromised root certificate.
The attack involves spoofing Yandex cloud server addresses on the router, after which the speaker receives a configuration with ADB enabled.
This allows disabling auto-updates and maintaining access after rebooting the device. The method has only been tested on the Mini 2 model.
Yandex confirmed the existence of the vulnerability and began distributing an update that closes the trust chain.
The new firmware automatically rejects compromised certificates, eliminating the possibility of remote network-based hacking.
8.4K views