 Exploit
Critical Signal Vulnerability Continues Data Transmission After Call Ends
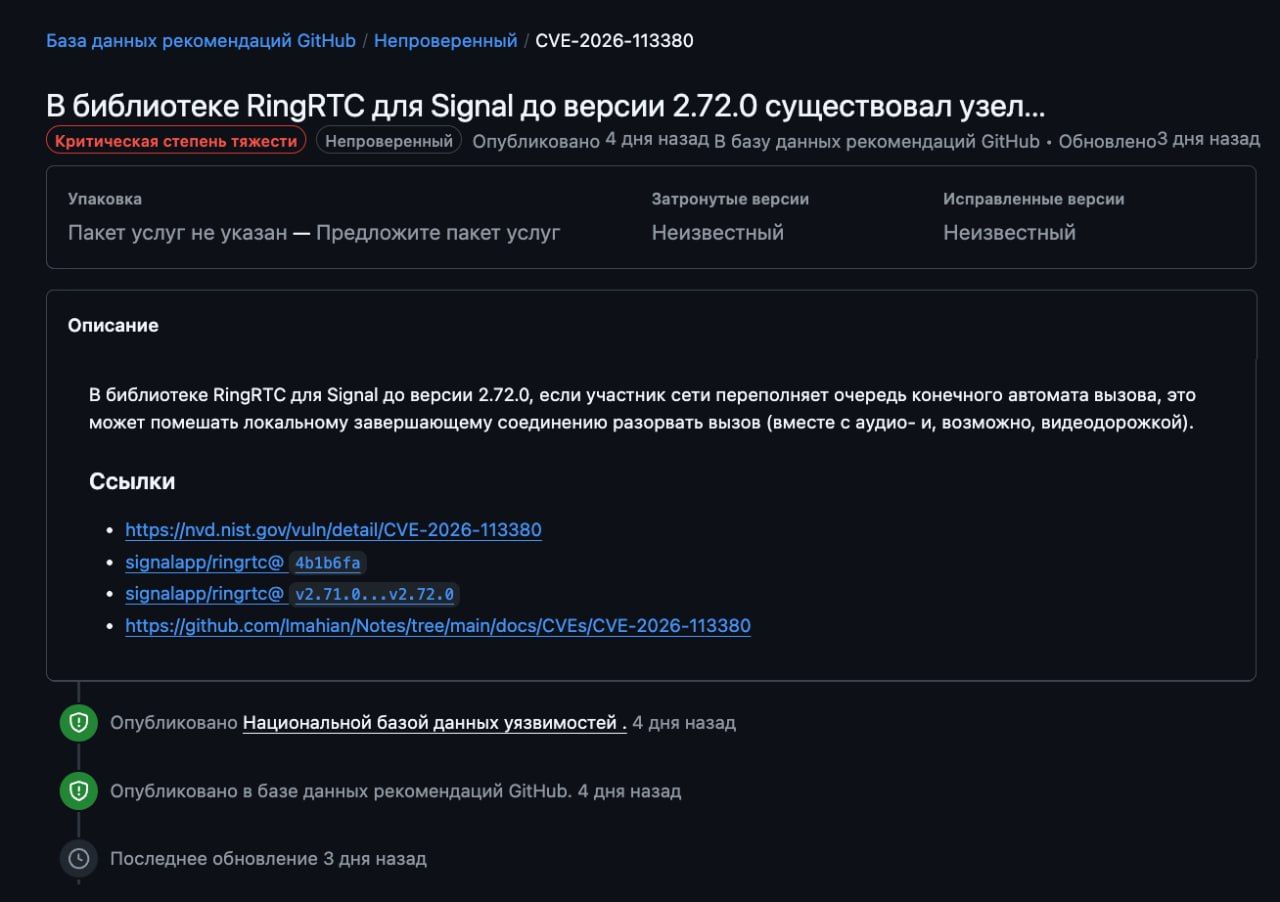
A critical high-severity vulnerability (9.3 out of 10) has been discovered in the Signal messenger. After users pressed the end-call button, audio and video streams continued to be transmitted to the other party.
The issue was identified in the RingRTC library up to version 2.72.0 inclusive. An attacker could intentionally clog the event queue on the other end of the connection, preventing the call termination command from triggering.
App developers released a patch to fix the bug as early as September this year. Users are advised to update to the latest stable version as soon as possible to protect their personal data.
22K views