 Crypto Headlines
Binance Hack: New Data on the Attack and Fund Theft
Binance Hack: New Details of the Attack and Fund Theft
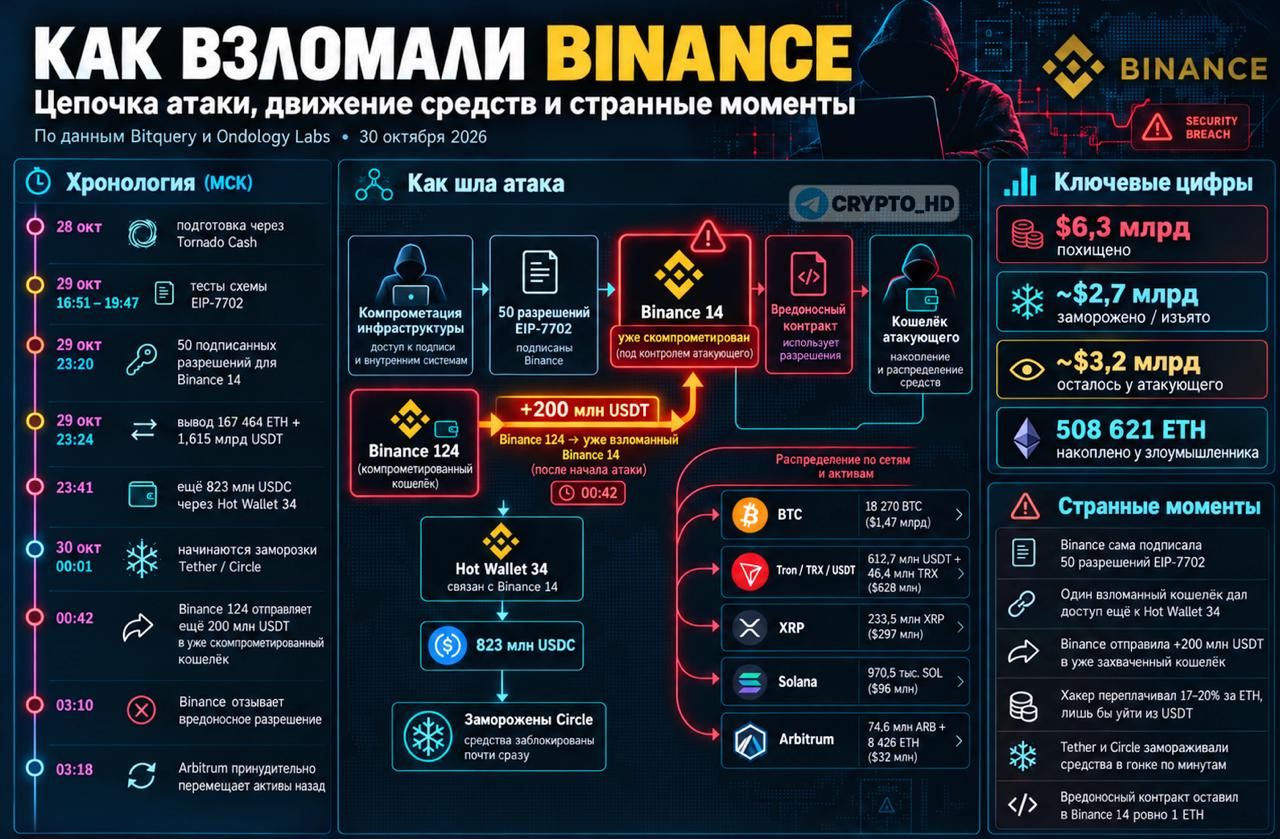
The Binance exchange transferred $200 million in USDT to a previously compromised Binance wallet. The hacker withdrew the assets in just 72 seconds to a frozen address; the exact mechanism remains unclear.
One compromised wallet granted access to another. Binance 14 held administrative privileges over an additional Binance 34 wallet.
For four full hours, funds from Binance clients—likely unaware of what was happening—were flowing into the hacked wallet.
The perpetrators rehearsed the Binance hack in advance. Preparations began at least on October 28 by funding wallets via Tornado Cash. The following day, the attacker tested the EIP-7702 mechanism on their own addresses.
Tether failed to freeze 6 out of 11 wallets in time; the hacker acted faster.
The group paid ~20% premium for Ethereum to exit USDT positions as quickly as possible. Within 35 minutes, wallets linked to the hackers exchanged $435 million USDT for 160,451 ETH.
Recently, Binance reported successfully repelling an attack by North Korean hackers (two days before this incident). They employed the Contagious Interview scheme: fake interviews and test tasks designed to trick developers into running malicious software.