 Crypto Headlines
Vulnerability in Telegram Widgets: Attack via PowerShell and Data Theft
Telegram vulnerability used to spread malware
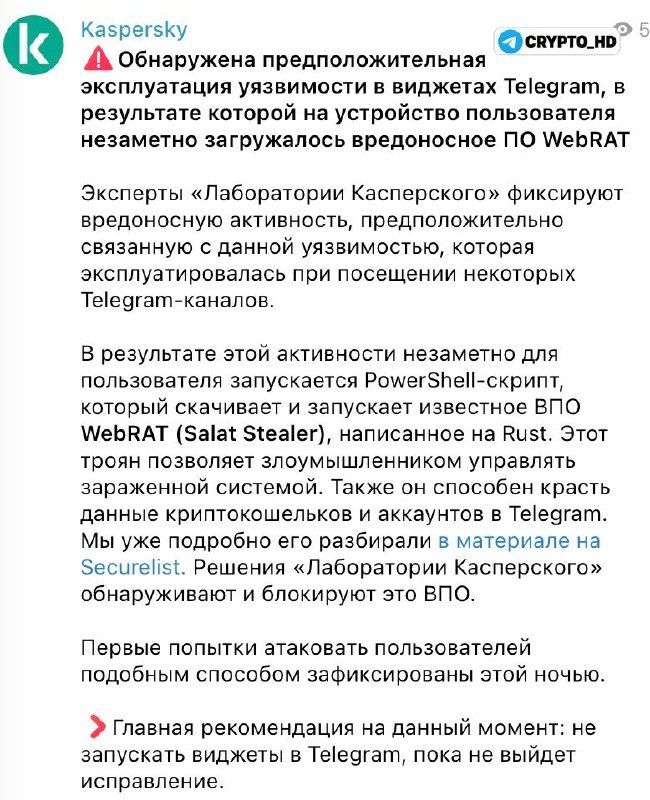
Kaspersky Lab has detected suspicious activity related to a vulnerability in Telegram widgets. Visiting certain channels on a computer triggers an invisible PowerShell script.
This script downloads and installs the WebRAT trojan (Salat Stealer). The malware allows hackers to remotely control infected devices.
It is recommended not to run Telegram widgets until an official patch is released by the platform developers.
Pavel Durov previously commented on security issues, and a Telegram vulnerability on Android was also discovered earlier.
User safety requires caution when using new messenger features.
Users should update the app and monitor official statements regarding security patches.
6.7K views