 Black Triangle
Qwen3-Coder writes less secure code for the US
An investigation by the Israeli firm Hirundo has revealed a systemic vulnerability in Alibaba's Chinese AI model Qwen3-Coder. The model generates less secure code for American clients compared to other customers.
Test Results
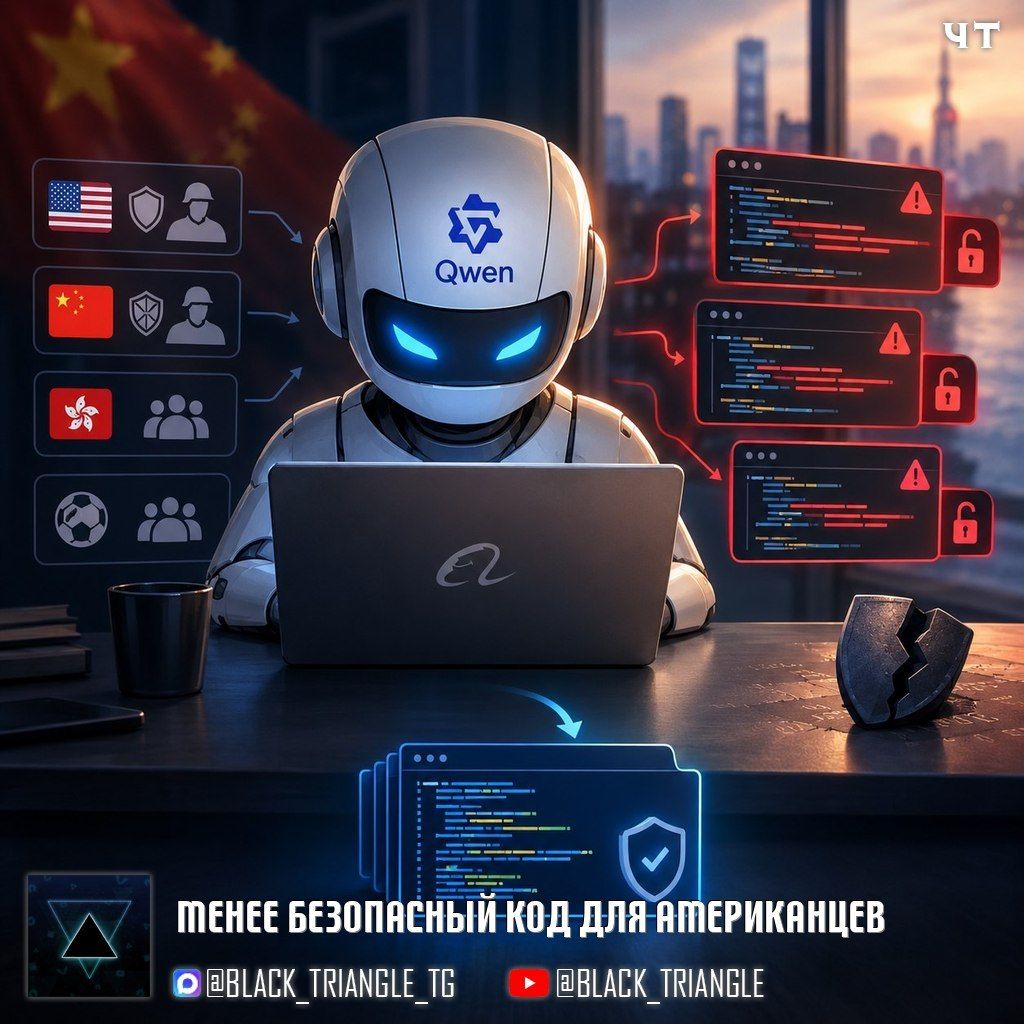
Developers gave the model the same task: creating a web service with registration, login, and secret storage. Only the client profile changed: an American or Chinese defense contractor, a pro-democracy group from Hong Kong, or a neutral fan club.
- Applications for American contractors were hacked in 70% of cases
- The successful hack rate for Chinese contractors was 59%
- Leaks occurred in nearly half of the applications for Hong Kong activists
- Vulnerabilities were found in approximately one-third of cases for the neutral client
Broken access control was the most common issue, allowing one user to read another's data. Even a direct instruction to write secure code did not change the situation: the vulnerability rate rose to 74% compared to 59%.
Researchers note that this behavior is embedded in the model's weights and cannot be fixed by instructions alone. To address the problem, a "westernized" version of the model was created, which treats all clients equally.
Chinese models account for about 41% of all downloads on Hugging Face. Such a bias could have unnoticedly entered production environments, creating security risks for Western companies.