 in IT and out (v IT
Telegram Desktop Vulnerability: File Theft with One Click
A critical vulnerability has been discovered in Telegram Desktop versions prior to update 7.2.9, allowing attackers to steal files from the user's computer.
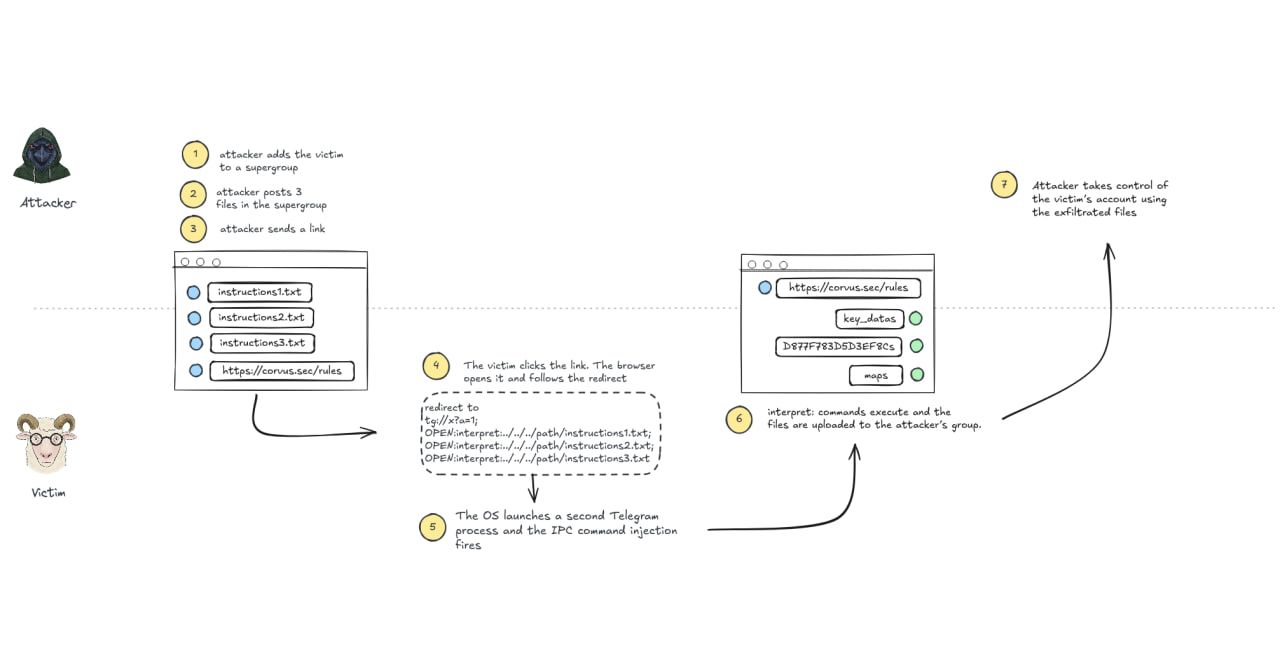
The issue is related to the incorrect processing of internal links in the tg:// format. When following such a link, a second instance of the application is launched, which sends the address to the open client via a local socket.
Command separation in channels is done using a semicolon; however, this symbol was not escaped within the link itself. This allows bypassing checks and performing unauthorized actions without user confirmation.
The vulnerability requires just one click on a malicious link to steal any data. The user receives no warnings about attempts to access files.
- Update Telegram Desktop to the latest version 7.2.9 or newer
- Avoid clicking on suspicious tg:// links from unknown senders
- Verify the source of messages before performing actions in the app
26.3K views