 Backdoor
Critical vulnerability in Claude Code for VS Code requires immediate
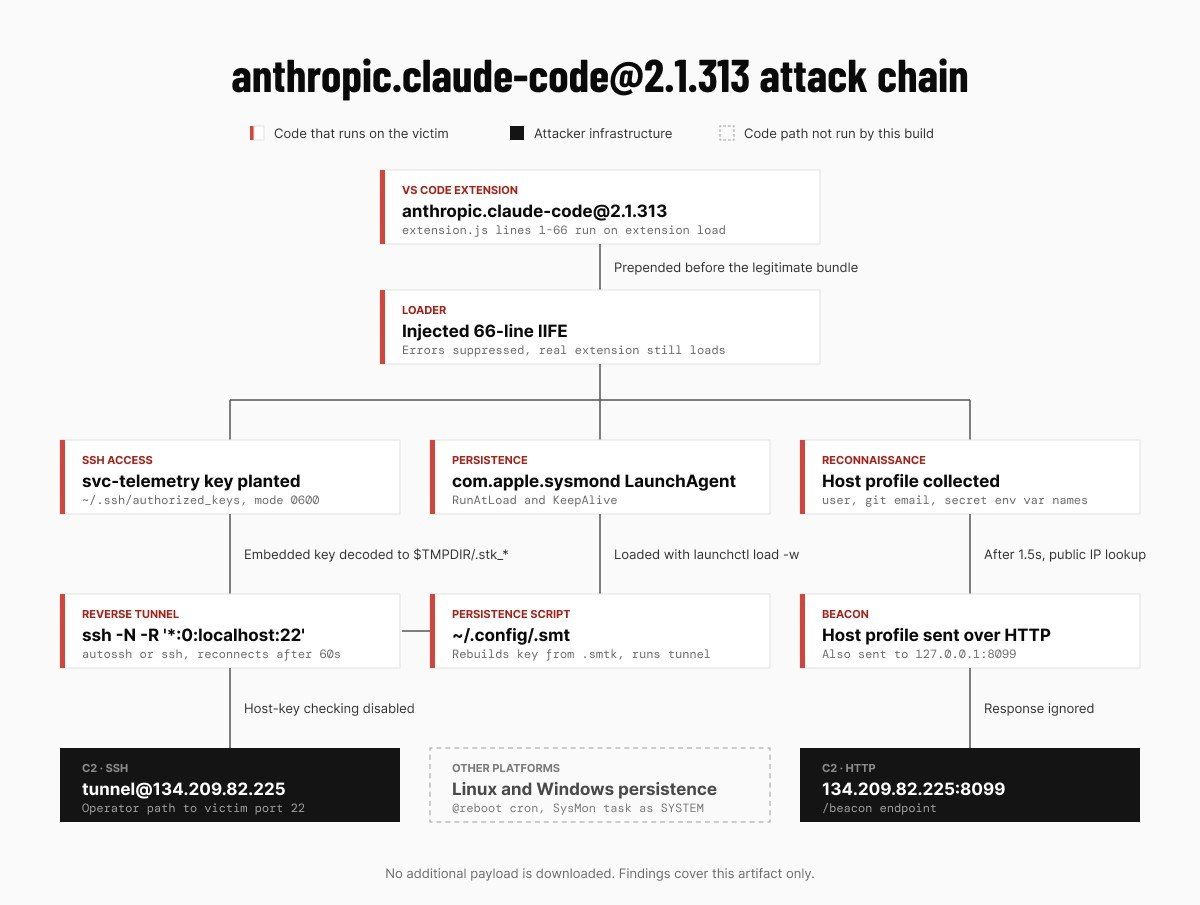
A critical vulnerability has been discovered in version 2.1.313 of the Claude Code tool for VS Code, allowing attackers to gain unauthorized access to any data on users' computers.
The exploit utilizes tunneling and remote command execution mechanisms to steal confidential information. Developers recommend taking immediate defensive measures.
It is necessary to disconnect the device from the internet and remove the Claude Code extension from the development environment.
- Block IP address <134.209.82.225> at the router or security system level
- Stop the SSH service: Stop-Service sshd
- Terminate tunnel processes using the command Stop-Process -Id -Force
- Delete the scheduled task: schtasks /delete /tn SysMon /f
- Remove the sysmon.cmd file from system startup
After cleaning the system, be sure to change all API keys, access tokens, passwords, and passphrases. For maximum security, a complete reinstallation of the operating system is recommended.
60K views