 Backdoor
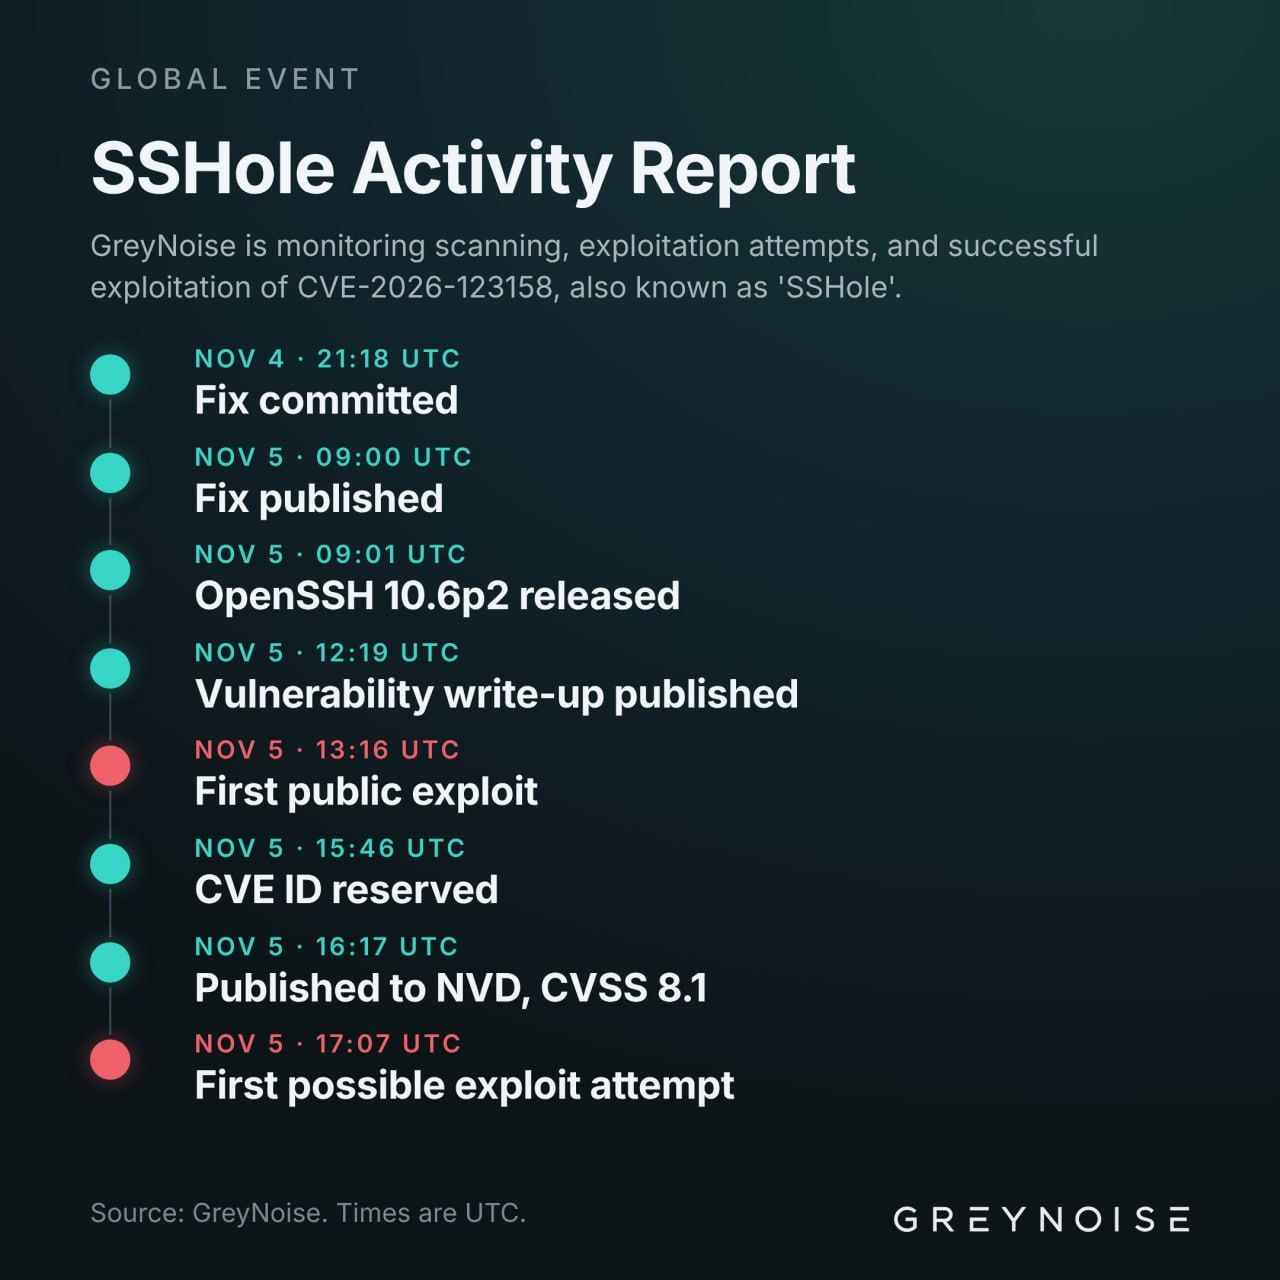
SShole Vulnerability in Alpine Linux: Passwordless SSH Key Installation
A critical SSHole vulnerability has been discovered in the Alpine Linux distribution, allowing attackers to install SSH keys for root and alpine users without a password.
Risk Conditions
- The openssh-server package is built without PAM support or uses openssh-server-pam with the UsePAM no parameter.
- Password login is enabled (PasswordAuthentication yes), which is the default setting in OpenSSH.
- There is an account with an asterisk (*) in the password field, such as root in the base image or alpine in tiny-cloud images.
- Any local account has a password hash of type $5$ or $6$.
The presence of at least one of the listed conditions makes the system vulnerable to unauthorized access right now.
66.2K views