 Crypto Headlines
PHP Vulnerabilities in the Crypto Industry: SlowMist Analysis
Cybersecurity researchers at SlowMist analyzed the security landscape in the cryptocurrency sector and discovered critical vulnerabilities across numerous industry resources.
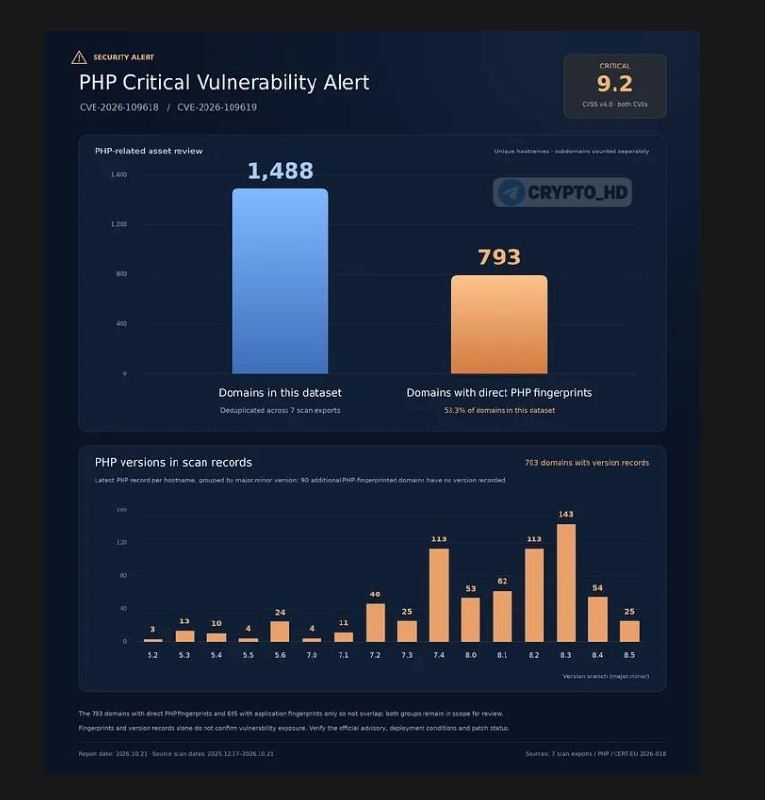
The analysis revealed that more than half of the checked websites use the outdated programming language PHP, creating serious risks for users and platform owners.
The SlowMist team audited 1,488 websites from the crypto industry. Signs of PHP usage were found on 793 of them (53.3%). This indicates the widespread distribution of vulnerable software.
Attackers can exploit these vulnerabilities to spoof recipient addresses, smart contracts, or transaction parameters. A user signs a transaction without suspecting fraud, without the need to hack the smart contract itself.
Through vulnerable servers of exchanges and crypto services, criminals could potentially access databases, API keys, and hot wallet management systems if they are poorly protected.
Sites using WooCommerce and payment modules such as Binance Pay, Crypto.com Pay, BitPay, CoinGate, and CoinPayments pose particular danger. Owners are advised to urgently install PHP patches.
It is necessary to check servers for traces of attacks and eliminate known vulnerabilities. Ignoring these measures can lead to the compromise of user funds and platform reputation.
11.1K views