 Black Triangle Channel Telegram
PS5 Jailbreak: Release of Relapse Exploit for Older Firmwares
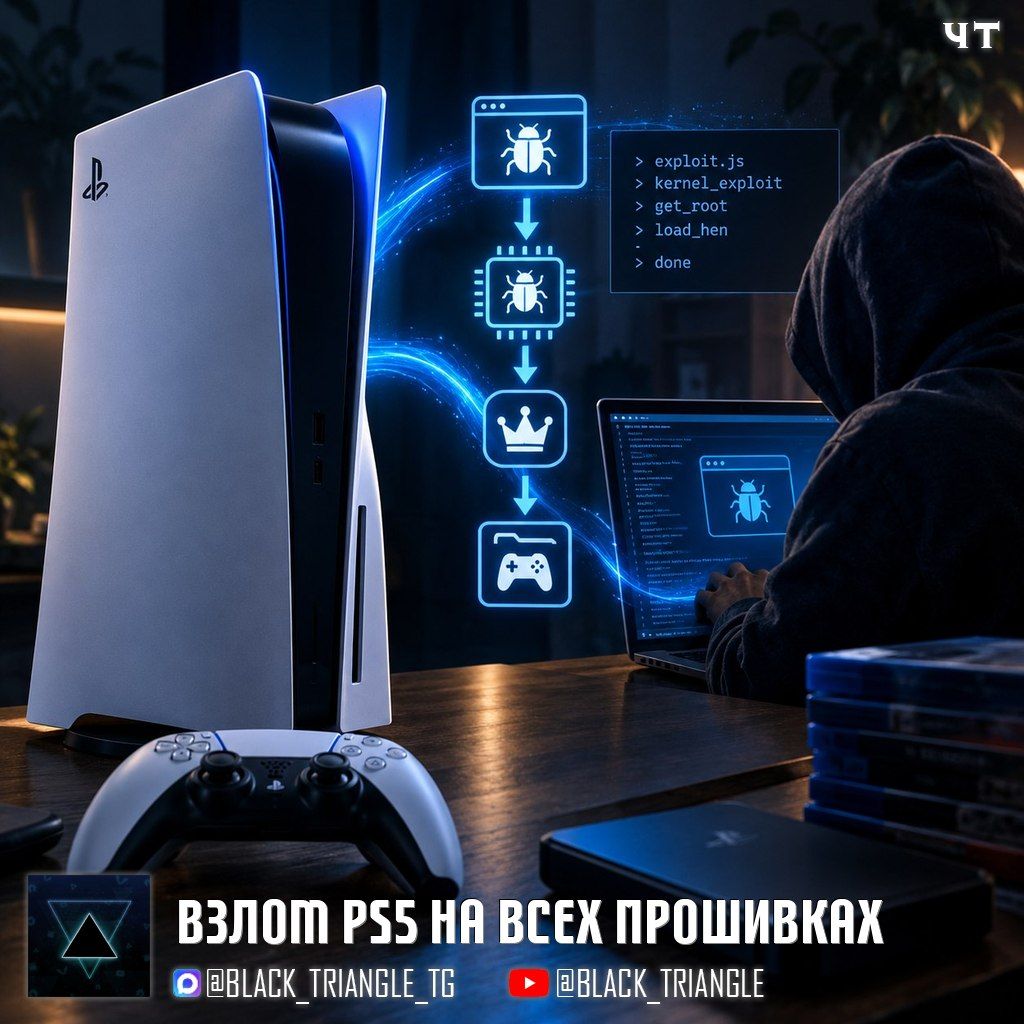
A developer using the pseudonym ntfargo has released a full exploit chain called Relapse for the PlayStation 5 console. The tool grants full system access and allows running homebrew applications on current firmware versions.
The exploitation of vulnerabilities occurs in two stages. First, an error is detected within the JavaScriptCore engine via the built-in browser, allowing memory reading and writing of the process. Then, a use-after-free vulnerability in the aio_multi_wait system call is leveraged to gain superuser privileges.
After escaping the sandbox, FreeBSD loads the etaHEN environment. This software is required to run homebrew applications, custom programs, and game dumps.
- The chain works on firmwares from version 7.00 up to 13.60
- The code is open-source under the MIT license for security research
- More than ten members of the PS-scene community contributed to its development
The exploit is characterized by instability: the browser component may require restarting, while the kernel component can cause the console to freeze or experience a kernel panic.
Sony has already patched these vulnerabilities in the 14.00 firmware update. Users who have updated their systems cannot apply the hack.
Using modifications violates Sony's terms of service. The manufacturer reserves the right to ban user accounts along with all purchased content.
The project's open-source code is available at the following link: