 Crypto Headlines
Massive Wave of Cyberattacks on Cloud Services and AI Infrastructure
The internet is facing a new wave of dangerous cyberattacks targeting cloud services and developer infrastructure.
What Happened
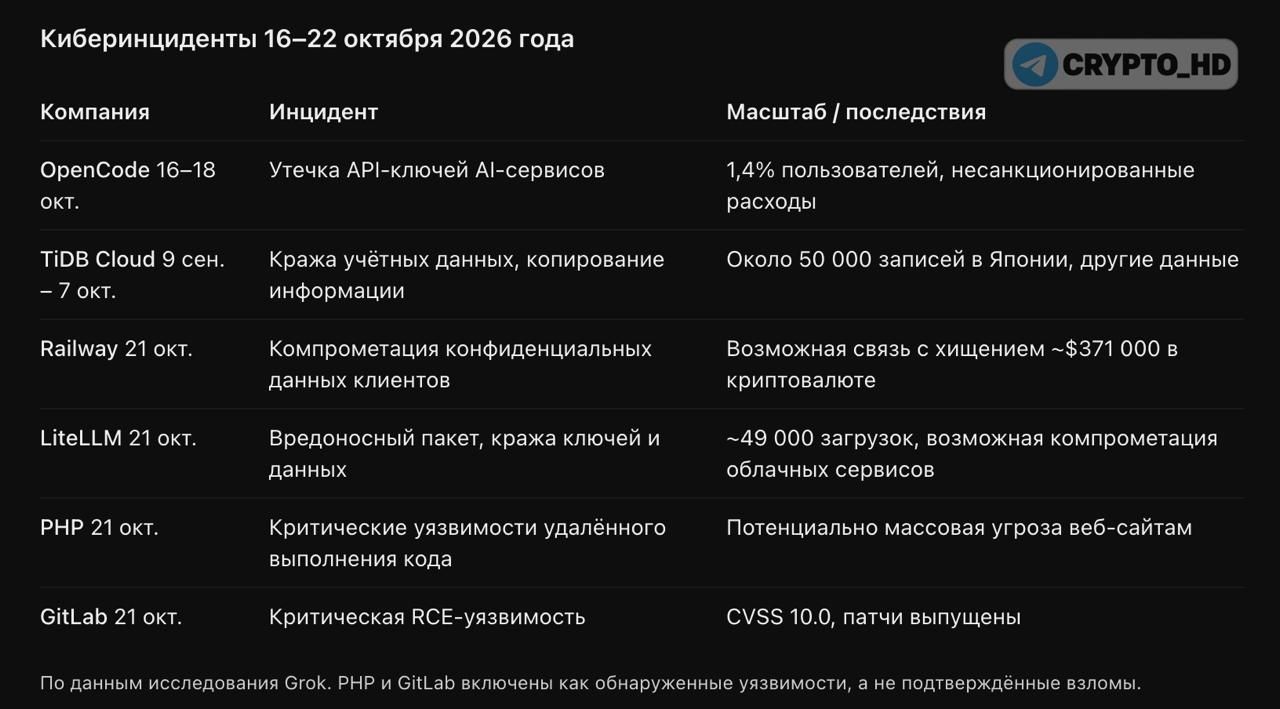
- Railway:* Attackers gained access to systems storing sensitive client data, including API keys and passwords. The company suspects the breach is part of a broader series of attacks on cloud services (link).
- Cryptocurrency thefts:* Researcher Taylor Monahan identified over 500 suspicious transactions across 19 blockchains totaling ~$371k. Suspected use of compromised private keys; possible link to the Railway incident (link).
- LiteLLM:* Reports indicate compromise of a software package for AI model integration. Malicious code was designed to steal API keys, cloud credentials, and other developer secrets (link).
- OpenCode:* Attackers stole AI provider API keys via an outdated system. The leak affected ~1.4% of users, running up charges on user AI accounts (link).
- PHP:* Critical vulnerabilities discovered allowing remote code execution on servers. Millions of sites are at risk.
- GitLab:* A critical vulnerability rated 10/10 has been identified, potentially allowing unauthorized remote code execution (link).
Key takeaway: Railway believes the breach may be part of a large-scale series of attacks on cloud services aimed at accessing AI infrastructure.
However, connections between these incidents remain unproven. The full scale of potential consequences remains unknown.
18.5K views