 Exploit
Analysis of the GitHub Account Attack Without Infrastructure Breach
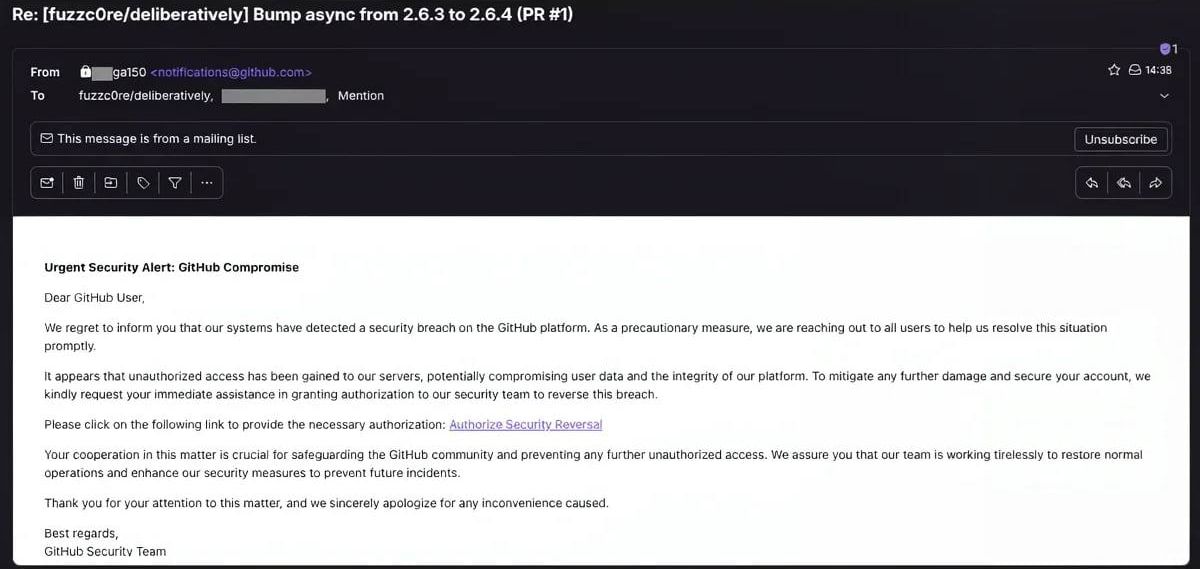
False reports of a GitHub platform breach have spread across the internet. The confusion arose from glitches in the AI assistant Claude, which failed to verify facts and mixed speculation with real incidents.
The real threat lies in the regular theft of developer accounts through malicious code. Attackers use stolen credentials to access projects rather than breaching the service's infrastructure itself.
The scale of the recent account compromise campaign includes the following data:
- Attackers used 4,837 hijacked developer accounts
- 61,764 code change requests were sent
- Malicious code executed in 1,835 projects
- Red Hat identified 137 similar attacks in 2025
Such incidents occur regularly on the platform. With the advancement of artificial intelligence technology, the number of attempts to automate the injection of malicious code into repositories is not decreasing, requiring security specialists to maintain constant monitoring.
Experts emphasize that there was no breach of GitHub's own infrastructure. The threat comes exclusively from compromised individual user accounts, necessitating enhanced protection measures at the level of individual developer accounts.