 Exploit
Critical Vulnerability in Telegram Desktop: File and Account Theft
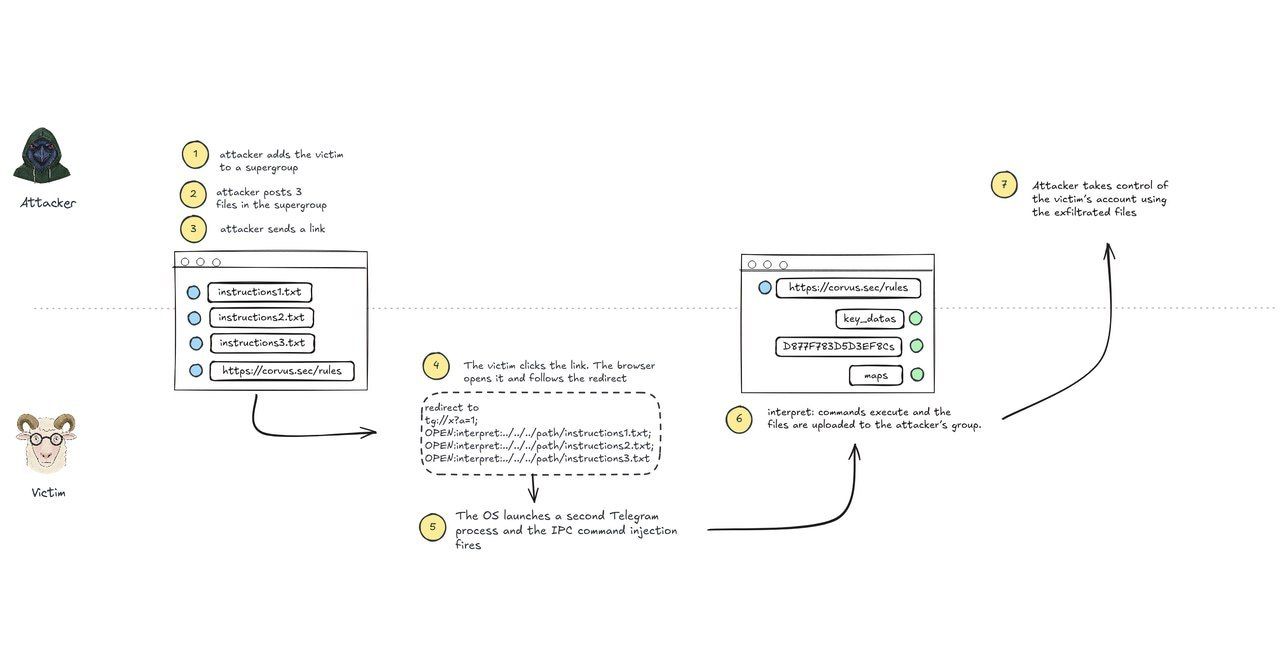
A critical vulnerability has been discovered in desktop versions of the Telegram messenger, allowing attackers to remotely steal files from the user's computer and take control of their account.
Attack mechanism based on exploiting the tg:// protocol
The vulnerability is related to the specific processing of links starting with the tg:// prefix. An attacker creates a special command that the victim may accidentally activate. When clicking such a link, malicious code gains access to the PC file system without any confirmation or notification from the user.
Ways to safely update the application
To eliminate the threat, users must install the latest version of the client as soon as possible. Official sources are available for different operating systems:
- Windows, macOS, Linux: official site desktop.telegram.org or GitHub repository github.com/telegramdesktop/tdesktop/releases
- Windows: Microsoft Store apps.microsoft.com/detail/9nztwsqntd0s
- macOS: App Store apps.apple.com/us/app/telegram/id747648890
- Linux: Flathub platform telegram.org/dl/desktop/flatpak and Snapcraft telegram.org/dl/desktop/snap
143.4K views