 Crypto Headlines
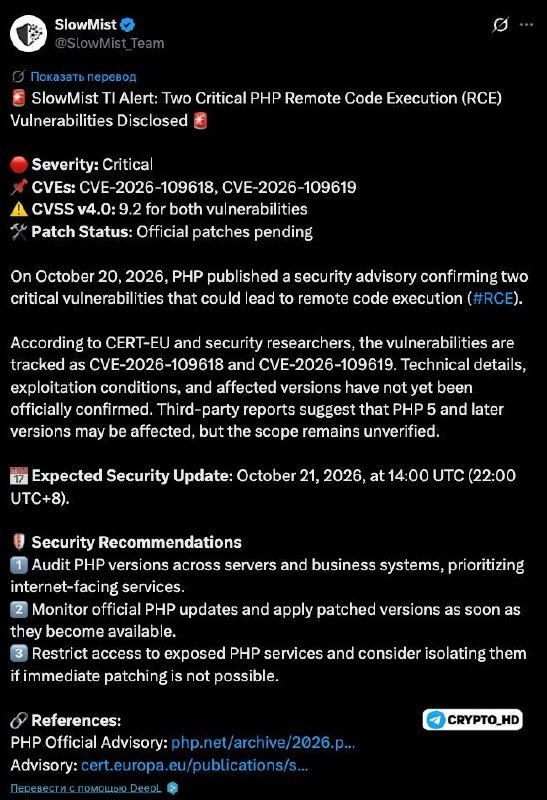
Critical Vulnerabilities in PHP: Remote Server Takeover Without Authentication
Two critical vulnerabilities have been discovered in the PHP programming language, allowing attackers to remotely take over servers without using a login or password. The security patch update will be released today at 14:00 UTC.
Critical Threat
PHP serves as the foundation for most websites and services on the internet. Almost all platforms running on this engine are at risk, including content management systems, online stores, admin panels, and landing pages.
Cryptocurrency exchanges, DeFi projects, and crypto wallets constitute a high-risk group. Hackers could exploit these flaws to gain full control over infrastructure without prior authentication.
List of potentially affected platforms:
- WordPress CMS and other content management systems
- E-commerce platforms such as Magento
- Admin panels and corporate websites
- Cryptocurrency exchanges and DeFi protocols
- Wallets and their interfaces
Protection Recommendations
The official PHP update is scheduled for today, October 20, 2026, at 14:00 UTC (17:00 MSK). Administrators are advised to immediately check the current version of their server software.
It is necessary to update the interpreter immediately after the official patch is published. This will close attack vectors related to remote code execution and unauthorized access.