 Black Triangle
Cryptographic Breakthrough: How AI Solved the NIST Mystery in 30
Anthropic's AI model Claude solved the mystery of the "random" numbers embedded in NIST elliptic curves over 25 years ago in just 30 minutes. These parameters are used in digital certificates and secure chips worldwide.
The origin of the seed values for standardized curves submitted to the US National Security Agency in 2000 remained a mystery due to lack of explanation. Trust in these numbers was shaken after the Dual_EC_DRBG generator scandal, which was suspected of containing backdoors.
Existing legends suggested the seeds were hashes of a developer's forgotten joke phrase. However, the AI model did not rely on these assumptions and independently conducted a cryptographic analysis.
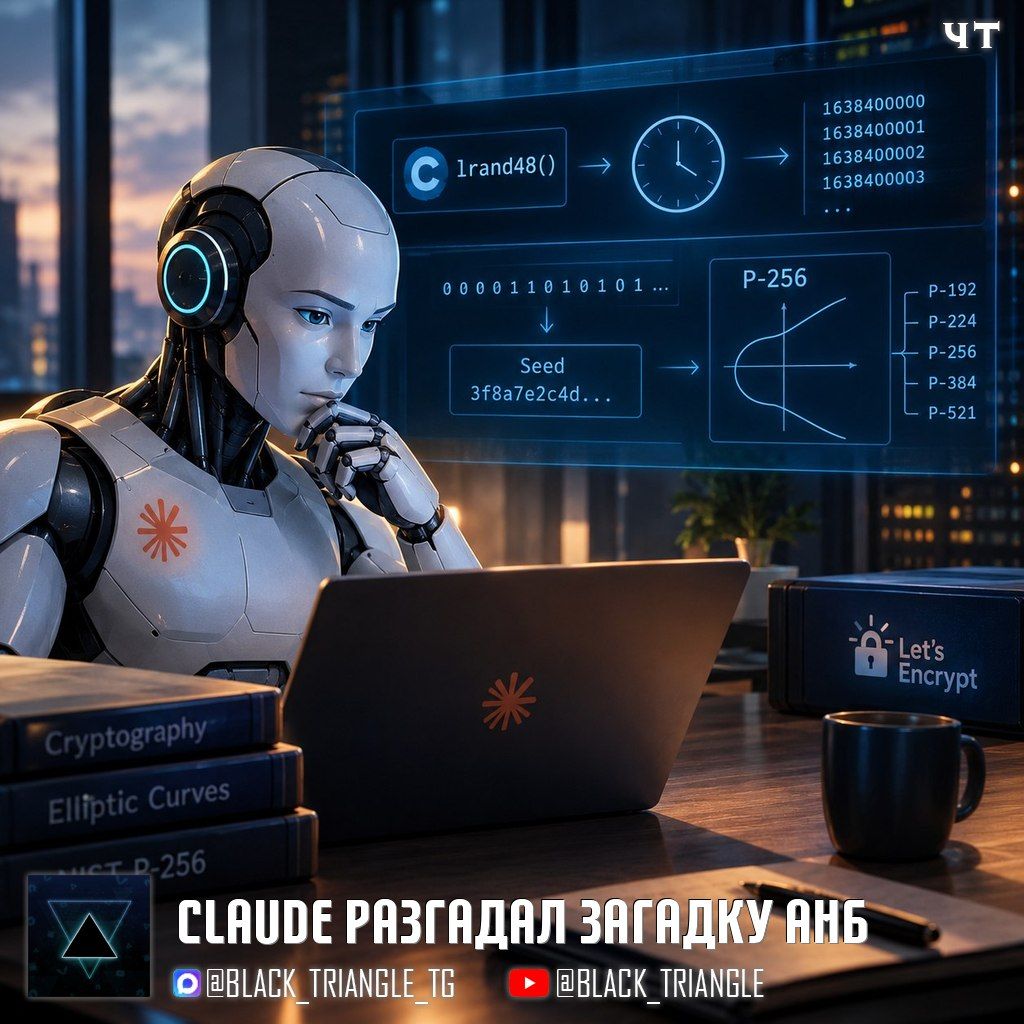
Analysis revealed traces of an old pseudo-random number generator: zero high-order bits in the data. The model reconstructed the sequence and identified the starting values as timestamps from the late 1990s.
The study results showed:
- The numbers were generated using the standard C library lrand48 function, seeded with system clock time
- The seeds for all five curves from P-192 to P-521 matched byte-for-byte
- Filippo Valsorda independently reproduced the generation in Go and confirmed the result's accuracy
In 2023, renowned cryptographer Filippo Valsorda offered a $12,288 prize for proof of these parameters' origin. With charitable donations, the amount increased to $36,864. Anthropic officially claimed the reward on October 15, 2026.
Anthropic decided not to keep the reward but transfer it to the non-profit ISRG, which supports the Let's Encrypt project. The solution addresses only the history of public parameters, not vulnerabilities in the curves themselves or the ECDSA algorithm.